An incident response plan for small business doesn’t need to be a 40-page enterprise playbook. You need a short, specific document that answers “what do we actually do” for the handful of incident types most likely to hit a business like yours, written down before you need it, not improvised during it.
Incident response plans get associated with enterprise-scale documentation: dozens of pages, elaborate escalation matrices, and roles most small businesses don’t have. That association is part of why so many small businesses never write one at all. The perceived bar feels too high to clear. A genuinely useful incident response plan for small business can be much shorter, as long as it answers the actual question that matters during a real incident: what do we do right now. NIST’s incident response guidance is a good reference if you want to see the full framework.
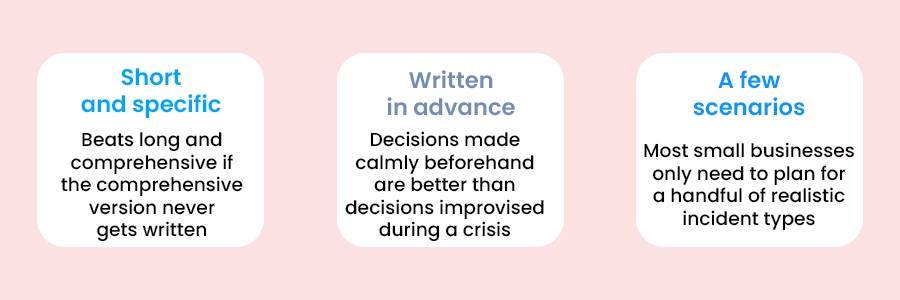
short and specific, Written in advance, A few scenarios
What Actually Belongs in an Incident Response Plan
Factor
Leasing
Buying
Upfront cost
Low — typically no large initial payment
Higher — full purchase price paid upfront or financed
Maintenance responsibility
Often included in the lease agreement
Typically the owner’s responsibility, sometimes covered by a separate service contract
Total cost over 5+ years
Often higher, due to ongoing lease payments
Often lower once the purchase price is fully amortized over a long usage period
Equipment refresh
Easier — upgrade to newer equipment at lease renewal
Requires a separate purchase decision to upgrade
Flexibility to change providers
Often locked into contract terms for the lease duration
Full flexibility — no contract tying you to a specific service provider
“What not to do” is often the most valuable section
During an actual incident, panic drives instinctive reactions — powering off a machine, deleting suspicious files, or restarting a system — that can destroy the evidence needed to understand what happened and whether data was actually affected. A short list of specific “don’t do this yet” items, decided calmly in advance, prevents some of the most common and costly mistakes.
Keeping Your Incident Response Plan Current
Keeping the plan actually usable
Review contacts and phone numbers at least twice a year.
Update it whenever a significant system or vendor relationship changes.
Walk through it once a year, even briefly, rather than assuming it’s still accurate.
Make sure more than one person knows where to find it.
For a basic version, not necessarily — but if your business handles regulated data or you want guidance on breach notification requirements specifically, involving legal counsel for that portion is worth it. The operational sections (contacts, immediate steps) don’t require legal review.
They’re related but distinct. Disaster recovery focuses on restoring systems and operations, while incident response focuses on the immediate actions during a security-specific event (detecting, containing, communicating). A short incident response plan for small business can reference your disaster recovery plan rather than duplicating it.
This is common and exactly why the contact list is the highest-priority section to write first — even identifying “we don’t currently have this relationship” is useful, since it flags a gap worth addressing before an incident happens rather than during one.
Conclusion and Next Steps
The goal of an incident response plan for small business isn’t a comprehensive document that covers every possibility. It’s a short, genuinely usable one that answers the specific questions a stressed, time-pressured team needs answered quickly. That’s achievable in an afternoon, not a multi-week project, and having something is meaningfully better than having nothing. Want help drafting yours? Talk to our IT team and we’ll walk through it with you.